Gap assessment
We assessed the company against ISO 27001, requirement by requirement, to measure the distance to certification.
ISO 27001 case study · B2B SaaS
A SaaS company kept losing enterprise deals at the buyer's security review. We ran its ISO 27001 program, from the first gap assessment to a certification audit it passed on the first attempt.
The challenge
The gap to the standard was one problem. The time of the people who would have to close it was the other.
ISO 27001 is the international standard for an information security management system (ISMS): the policies, controls and records a company uses to manage its security risks. An independent certification body audits the company against it and decides whether to issue the certificate.
What we did
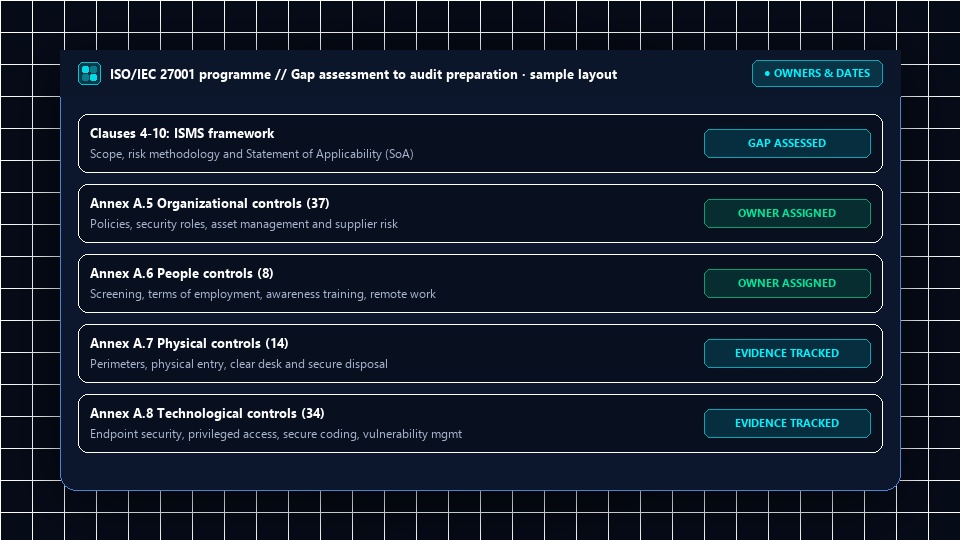
A policy pack (a folder of templates with the company's name filled in) produces documents, but auditors want evidence that controls are operating. That evidence comes from people inside the company doing the work week after week, so we ran the program as a project with owners and dates.
We assessed the company against ISO 27001, requirement by requirement, to measure the distance to certification.
We designed the controls around how the company works. Each control got an owner inside the company: one of the client's own staff, not us.
We tracked evidence collection against those owners and dates. Then we prepared the company for the certification audit.
The impact
The company now has ISO 27001 certification to show at the enterprise security reviews where its deals had been stalling. The figures are the client's own, as reported to us.
The hard part
The timeline held for one reason, and it wasn't us. The client committed internal owners, and those owners did the work.
We don't issue certificates. An independent certification body runs the audit and makes that call. Our job is getting the company ready for it.
Related services
Start with the question your buyers are asking.
More case studies: bank security assessment, patient care management app, hotel management platform and logistics operations platform. Or see every case study.

Let's talk
Tell us which certificate your buyers ask for and who on your side can own the work. We reply within one working day.